ISO/IEC 27001:2022 · Leadership in information security and data protection
ISO/IEC 27001 Information security certification
For technology companies, banks and service providers: protects your data and your clients' data.

 recognised through
 and registered with
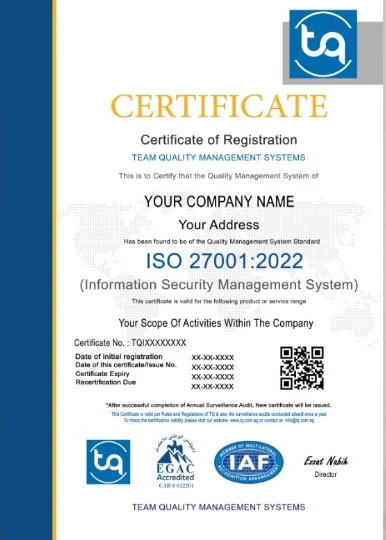
Overview
What is ISO/IEC 27001 certification?
ISO 27001 is an internationally recognised standard for information security management systems (ISMS). Certification shows that an organisation applies effective practices to protect sensitive data and information from threats and breaches. The standard aims to safeguard the confidentiality, integrity and availability of information, helping to protect an organisation's digital assets and meet legal and regulatory requirements.
ISO 27001 sets out a range of controls and procedures for organisations to follow, including risk analysis, information security policies, access control, encryption and incident management. Implementing the standard reduces security risks, builds trust with customers and partners and improves operational efficiency, which in turn strengthens the organisation's reputation and opens up wider opportunities in global markets.
Your route to information security compliance
Achieve reliable protection and full compliance with data security standards through clear, straightforward steps.
Your path to innovation and digital trust
ISO 27001 helps you secure digital innovation and increase customer and partner confidence in your services.
Better protection for your data and information
Certification strengthens the security of your systems and makes your data better protected and more resilient. Find out how to achieve it.
The key to success in a data-driven world
The foundation for high-level information security that opens up opportunities in local and international markets.
What does ISO/IEC 27001 bring your organisation?
The key benefits organisations gain from implementing the standard and achieving certification.
-
Stronger information security
ISO 27001 helps protect your sensitive data from unauthorised access, leakage or damage.
-
Reduced cyber risk
Certification helps you identify and address security vulnerabilities before they become real threats.
-
Legal compliance
Certification makes it easier to comply with laws such as the GDPR and other data protection legislation.
-
Greater customer and partner trust
Certification demonstrates your commitment to protecting customer and partner information, building confidence in your services.
-
New markets and opportunities
Compliance with ISO 27001 opens the door to contracts with major organisations that require high security standards.
-
More efficient internal systems
By documenting policies and procedures and clearly defining security responsibilities.
-
Higher customer satisfaction
By securing customers' data and reassuring them that their transactions take place in a reliable and secure information environment.
-
Stronger risk management
The standard helps you develop a systematic approach to assessing and treating information security risks effectively.
-
Competitive advantage
Certification gives you a competitive edge, particularly in sectors that demand high security commitments.
-
Enhanced corporate reputation
Achieving ISO 27001 reinforces your image as a trusted organisation that takes care to protect its own information and that of its customers.
How to get ISO/IEC 27001 certified
A clear path from first contact to receiving your certificate, with support afterwards.
-
1
Step 1: Initial enquiry
Our team explains the certification process and the requirements for ISO 27001 certification, and sends you a quotation.
-
2
Step 2: Pre-assessment (optional)
An optional pre-assessment audit shows where your information security management system stands against the standard before certification.
-
3
Step 3: Stage 1 and Stage 2 audits
We review your ISMS documentation and readiness (Stage 1), then audit how your security policies and controls work in practice (Stage 2).
-
4
Step 4: Certification
Once the audit confirms that the requirements are met, your organisation is awarded ISO 27001 certification.
-
5
Step 5: Surveillance audits
Annual surveillance audits, and recertification every three years, confirm that your organisation continues to meet the standard.
Free, no-obligation enquiry
Ready to start your ISO/IEC 27001 journey?
Tell us about your business and number of branches, and we'll send you a tailored quote, the steps and the expected timeframe.
ISO/IEC 27001 frequently asked questions
What is ISO 27001?
ISO 27001 is an internationally recognised standard for information security management. It aims to protect the confidentiality, integrity and availability of information through an integrated management system that identifies and treats security risks.
What are the main benefits of ISO 27001 certification?
Benefits include protecting sensitive information, building trust with customers and partners, complying with legal requirements such as the GDPR, and reducing the likelihood of breaches and cyber attacks.
Does every organisation need this certification?
It is not mandatory, but it is recommended for any organisation that handles sensitive data or wants to strengthen its cyber security and credibility with customers.
What are the main steps to ISO 27001 certification?
The steps include a gap analysis, risk assessment, developing policies and procedures, implementing the information security management system, internal audit, and finally assessment and certification by an accredited certification body.
How long is ISO 27001 certification valid?
It is usually valid for three years, with annual surveillance audits to confirm ongoing conformity with the standard.
What is the difference between ISO 27001 and ISO 9001?
ISO 27001 focuses on information security and the management of related risks, whereas ISO 9001 covers general quality management systems for all types of organisation.
Does ISO 27001 certification require compliance with other standards?
Not necessarily, but it can be useful to integrate ISO 27001 with standards such as ISO 9001 or ISO 22301, depending on the nature and needs of your organisation.
Does my organisation have to be large to achieve ISO 27001?
No. Organisations of all sizes, including small and medium-sized enterprises, can be certified provided they can meet the requirements and implement the system effectively.
How long does it take to achieve ISO 27001 compliance?
It depends on the size of the organisation, the complexity of its processes and its level of readiness. On average, the process takes 3 to 6 months.
Can I use ISO 27001 certification to promote my services?
Yes, absolutely. Certification reflects your commitment to protecting customer data and strengthens your image as a trusted, secure organisation.
Related standards
Many organisations combine several standards into one integrated management system with a single audit.
-
9001
ISO 9001:2015
Quality management
For any organisation: controlled processes and customer satisfaction. Required in most tenders.
Standard details -
45001
ISO 45001:2018
Occupational health and safety
Protects your workforce and reduces workplace accidents and downtime on sites and in factories.
Standard details -
22301
ISO 22301:2019
Business continuity
A tested plan that keeps your business running through crises and sudden disruptions.
Standard details -
20000-1
ISO/IEC 20000-1:2018
IT service management
For IT service providers: well-organised services with measurable quality.
Standard details